Cookie sessions with CSRF instead of tokens in JavaScript — required for a real checkout and admin on production domains.
Payments as a state machine: signed webhooks, atomic stock, emails, and retry — not a Checkout.js snippet.
One FastAPI surface for storefront and admin, split by domain (catalog, orders, cart, coupons, shipping), not by client.
What I built
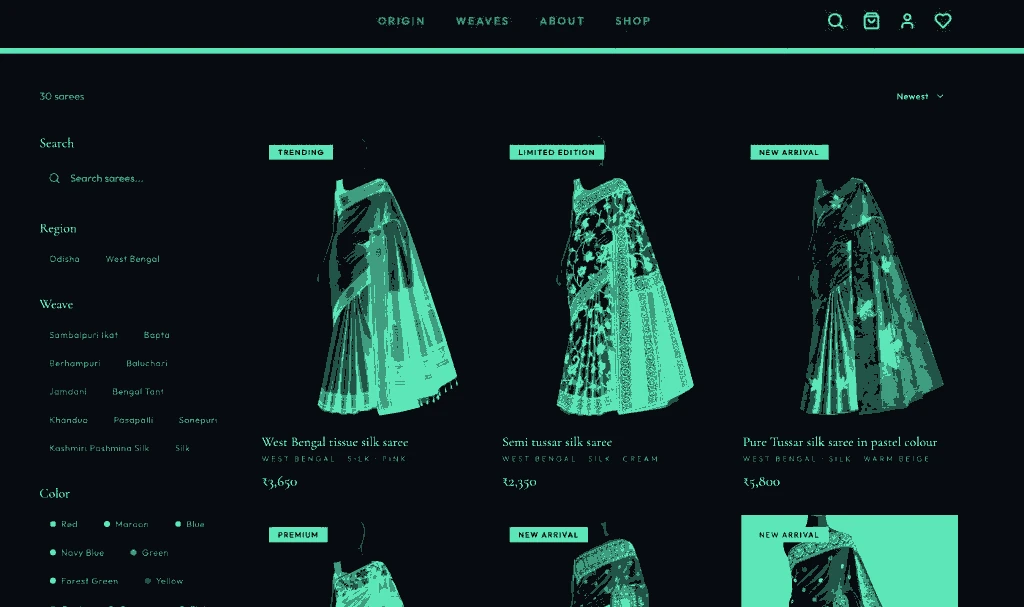
Storefront: ~18 routes — narrative landing, shop with filters and infinite pagination, PDP, cart/wishlist, checkout (shipping + coupons + Razorpay), account with payment retry, OTP/email auth, legal and SEO (JSON-LD, sitemap, OG).
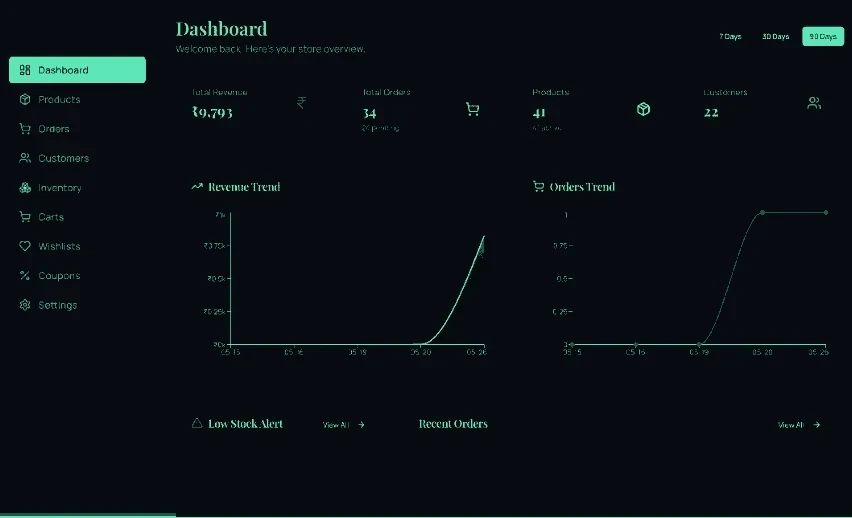
Commerce API: 15+ domains — auth, customers, products and variants, orders and webhooks, cart, wishlist, coupons, shipping, taxonomy, assets, health — with pagination, batch joins (no N+1), and cache invalidation.
Razorpay end-to-end: create order → Checkout.js → signed webhook → atomic stock decrement → confirmation email. Cancel restores stock. Pending orders can be reinitiated from the account.
HttpOnly JWT cookies plus CSRF; Redis rate limits on auth, search, cart, and admin; CORS with credentials.
Media: Azure Blob upload → Pillow multi-size WebP → CDN URLs. Shipping zones and free-threshold config in admin, calculated at checkout.
Took a generative scaffold to production: Docker, GitHub Actions, Redis, and a deploy path that actually runs.
Outcome
Live and taking orders. Private walkthrough on request.